The most serious flaw of the week affects SonicWall firewalls, very common in small and medium businesses, and specifically their SSL VPN, the door through which employees and suppliers enter the company network from outside. It is CVE-2026-19868, and it lets an attacker bypass the VPN's SAML login and, with it, the multi-factor authentication (MFA) enforced through SAML.
It is already exploited in real attacks: the US CISA added it to its catalogue of exploited vulnerabilities (KEV) on 6 November, the same day it was published, and on 9 November CSIRT Italia also reported exploitation in the wild.
What happens
Many companies let users into the VPN with a SAML login: the password and the second factor (code, app, push notification) are checked by an external identity provider such as Microsoft Entra ID or Okta. That is exactly the check meant to stop someone who only has a stolen password.
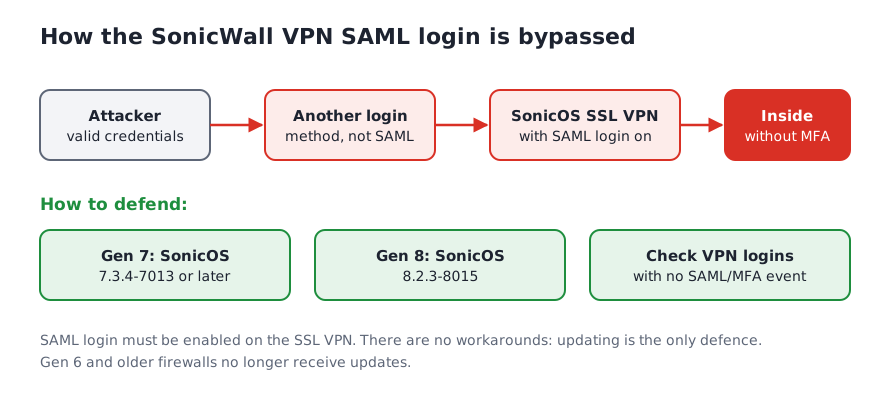
According to SonicWall, the SonicOS SSL VPN service does not fully enforce that check: a user with valid credentials for another login method configured on the firewall can skip SAML and, if MFA is enforced through SAML, skip MFA as well.
Two things to keep in mind:
- it is not an unauthenticated bypass: a valid password is needed, for example for an account on the firewall that uses a method other than SAML;
- the flaw only matters if SAML login is enabled on the SSL VPN. But that is exactly the setup of anyone who wanted to protect the VPN with MFA.
Who is affected
SonicWall Gen 7 and Gen 8 firewalls, physical and virtual, with these SonicOS versions:
| Firewall | Affected versions | Fixed version |
|---|---|---|
| Gen 7 | 7.3.3-7015 and earlier | 7.3.4-7013 or later (7.3.4-7015 came out on 5 November) |
| Gen 8 | 8.2.2-8015 and earlier | 8.2.3-8015 |
The same update fixes six other SonicOS flaws, none reported as exploited: SonicWall gives the set a CVSS score of 8.8 (high), while for this flaw CISA calculates 7.5.
What to do
- Update now to SonicOS 7.3.4-7013 or later (Gen 7) or 8.2.3-8015 (Gen 8), downloading the firmware from MySonicWall. There are no workarounds: updating is the only defence.
- Check VPN access. Compare successful SSL VPN logins with your identity provider's logs: a VPN login without a matching SAML and MFA sign-in may be a sign of an attack.
- Reset the credentials of accounts involved in suspicious logins, including the firewall's local accounts, and remove the ones you no longer need.
On PatchRadar you will find the flaw's page, the CSIRT Italia alert, the versions per branch in SonicWall SonicOS (for example 7.3 and 8.2) and every flaw already exploited in Exploited now.
Sources: SonicWall, SonicOS 7.3.4 and 8.2.3 Security Advisory · NVD, CVE-2026-19868 (with CISA KEV catalogue data) · CSIRT Italia, exploitation of CVE-2026-19868 · Help Net Security, exploited SonicWall SSL VPN flaw